A key for every company
Report content, messages and files are encrypted with AES-256-GCM, using a separate key for each company, itself wrapped by a master key.
Each company's reports are encrypted with its own key, reporter identities are sealed with another, and SpeakUpSafe's own tools can only count. Here is how, and where the data goes.
Report content, messages and files are encrypted with AES-256-GCM, using a separate key for each company, itself wrapped by a master key.
Who reported is kept in a separate vault, sealed with its own key. A confidential name opens only with a second person's approval, and the reporter is told.
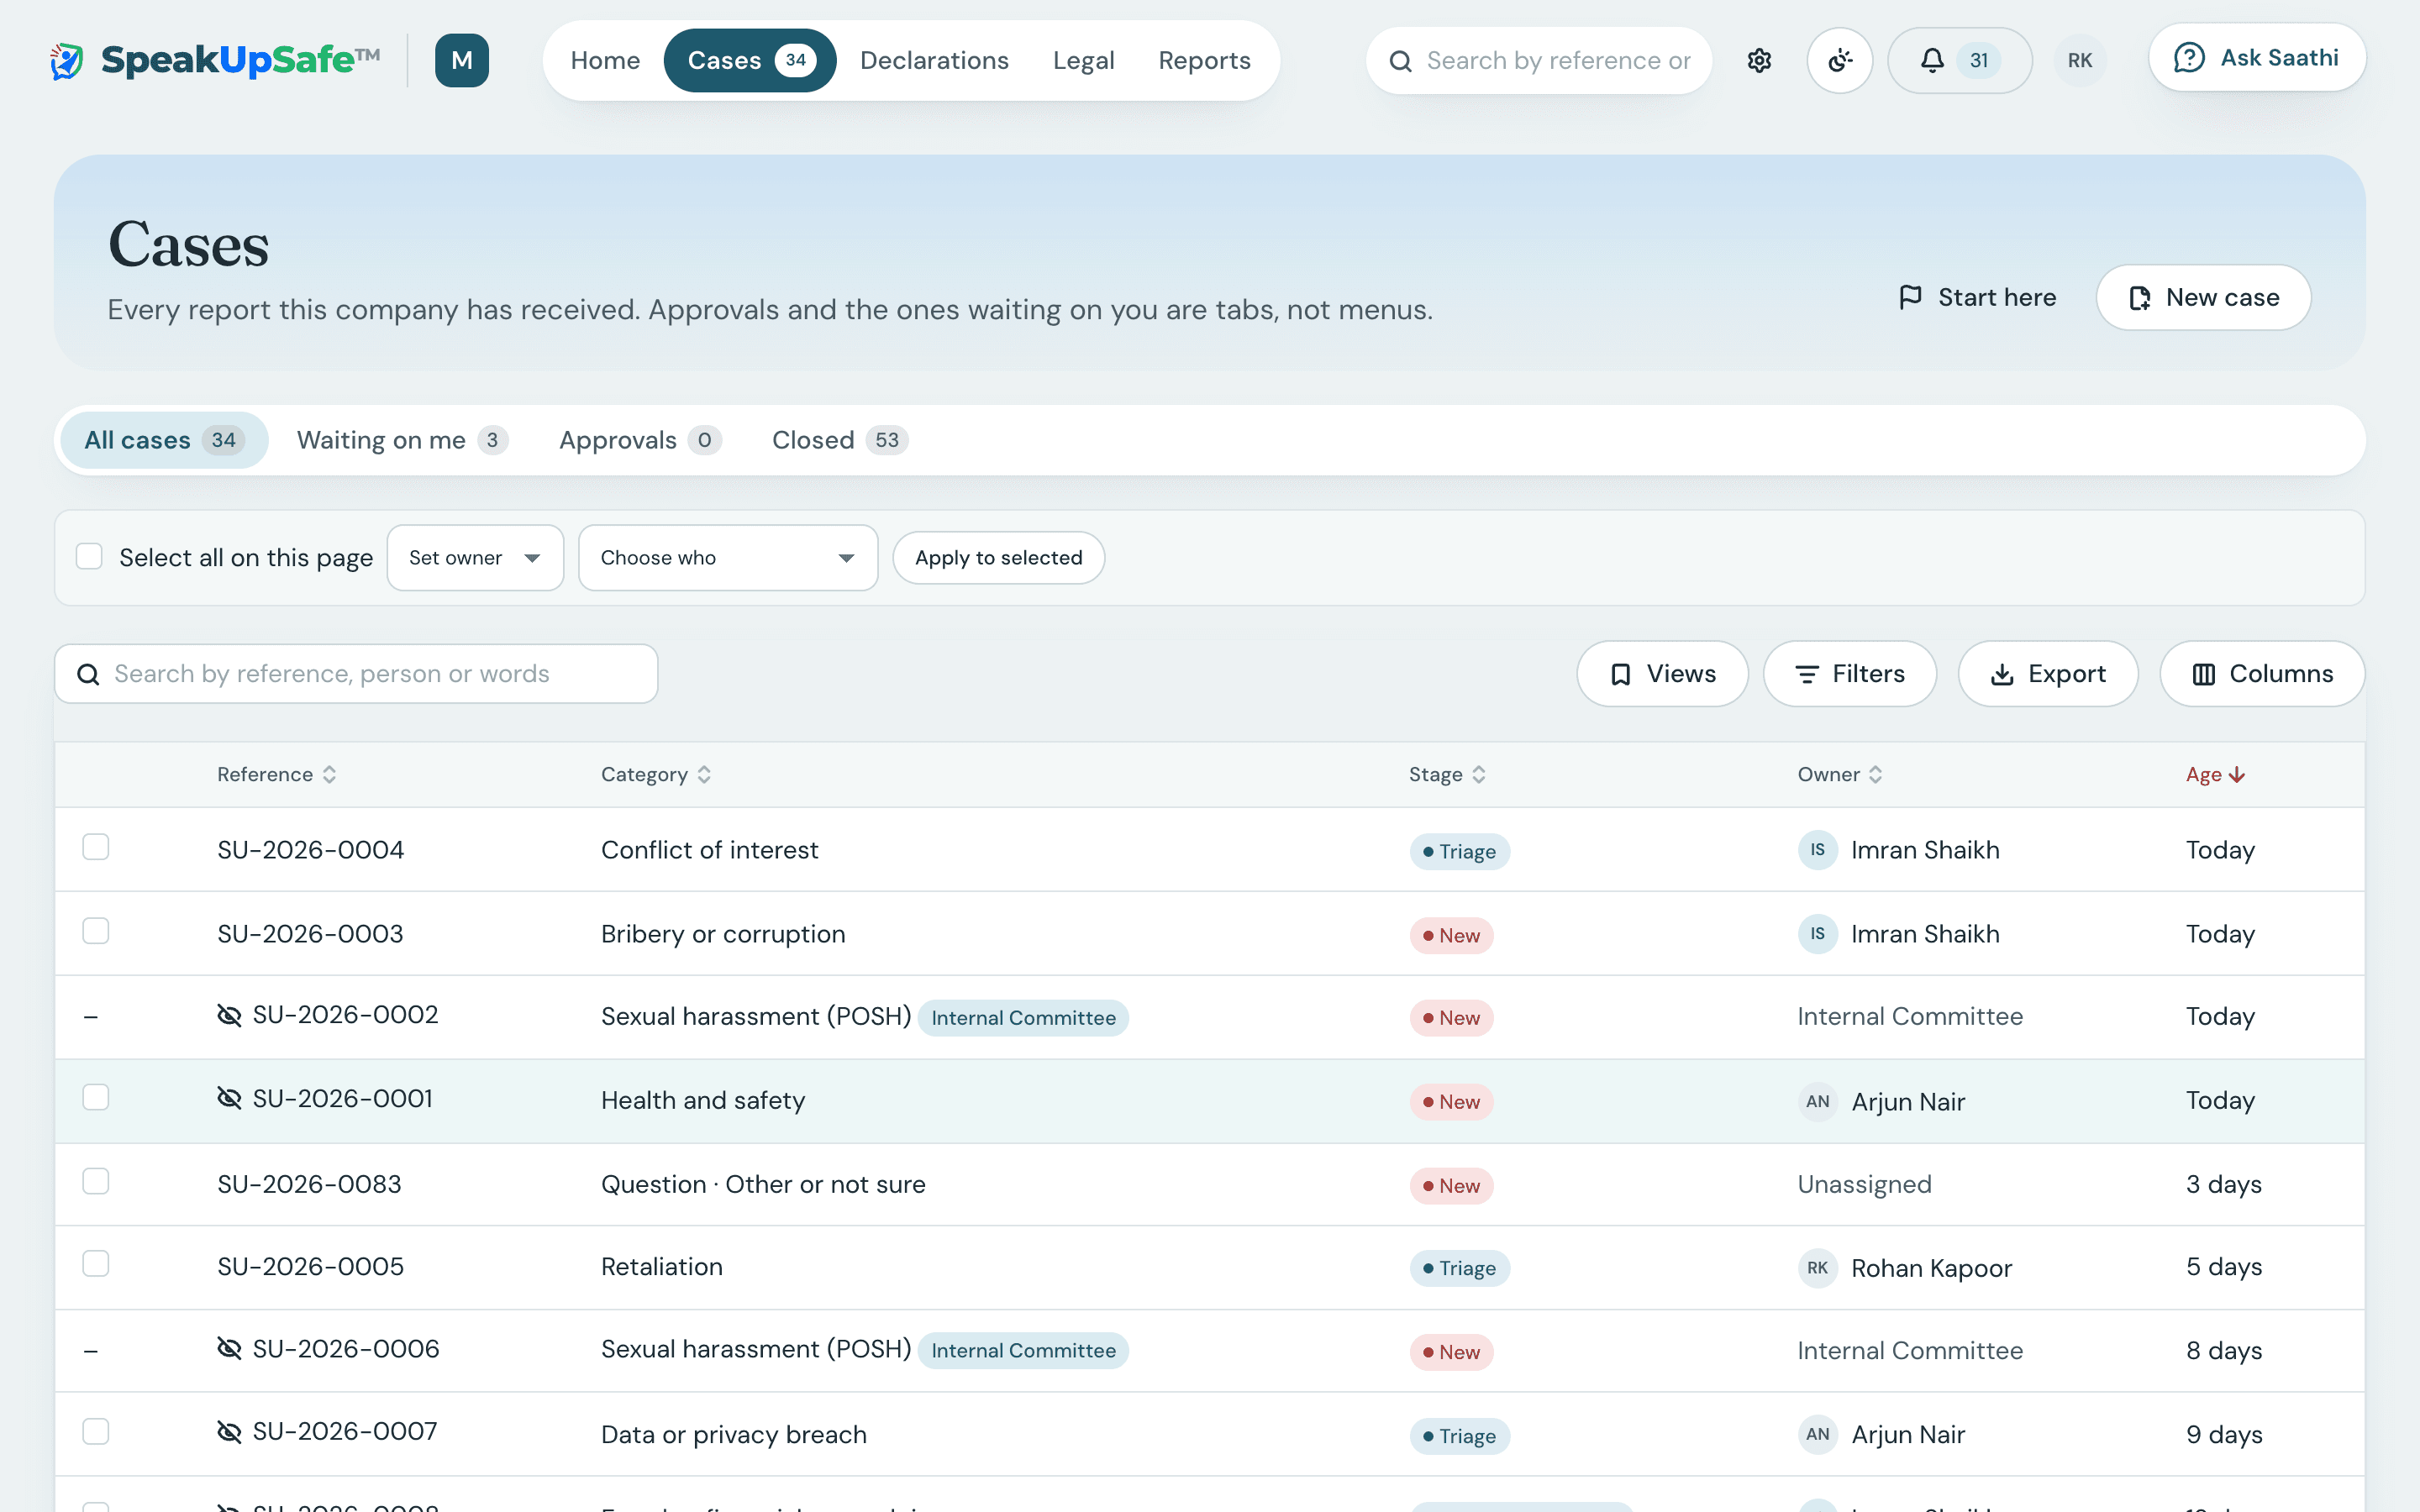
Every action on a case, in admin and by automation goes into an append-only log where each entry carries the fingerprint of the one before. The chain can be checked at any time.
Our console reads through a database role that can only return counts. Support can open a company's settings only with its admin's consent, for a set time, with every action logged, and never a case.
Each upload is checked by its content, stripped of hidden details such as location, fingerprinted, kept in private storage, and every download is logged.
Retention per company and per category (7 years by default), then anonymised or deleted. A legal hold pauses it. Data requests have their own register with the legal due dates.
What it asksReasonable security safeguards, erasure once the purpose is served, and the rights of the people the data is about.
What the product doesEncryption per company, retention per category, a register of data requests with their due dates, and an employee's data exported or erased from admin.
What it asksThe reporter's identity kept confidential, personal data handled under the GDPR, and records kept no longer than needed.
What the product doesSealed identities, need-to-know access inside the case team, and retention that runs by itself.
What it asksSecurity suited to the risk, including encryption and the ability to show it works.
What the product doesEncryption at rest per company, the audit chain check, and a controls register mapped to ISO/IEC 27001 and SOC 2.
What it asksLogs kept, and cyber incidents reported within 6 hours.
What the product doesCase team sign-ins are logged for this, and referrals carry the CERT-In deadline. Reporters' internet addresses are never kept.
A summary, not legal advice. Your lawyers will know which rules apply to your company.
A walkthrough of the screens on this page, set up around your company.